Rapid intervention for hacked, blacklisted, or compromised websites. Deep forensic cleanup, root-cause vulnerability patching, and search engine blacklist delisting.
Reply within one working day · Fixed quote in 5 days · No sales decks
Engagement overview
Book a technical discovery session with our senior engineering lead.
Recovery services include:
Good fit if
Businesses facing urgent website defacement, malicious redirects, spam injections, or Google Safe Browsing warnings.
Securing the server, revoking unauthorized access, and halting active data exfiltration.
Removing backdoors, malicious PHP shells, rogue admin accounts, and hidden scripts.
Submitting formal review requests to Google Search Console to clear security warnings.
Configuring Cloudflare WAF rules, hardened file permissions, and intrusion monitoring.
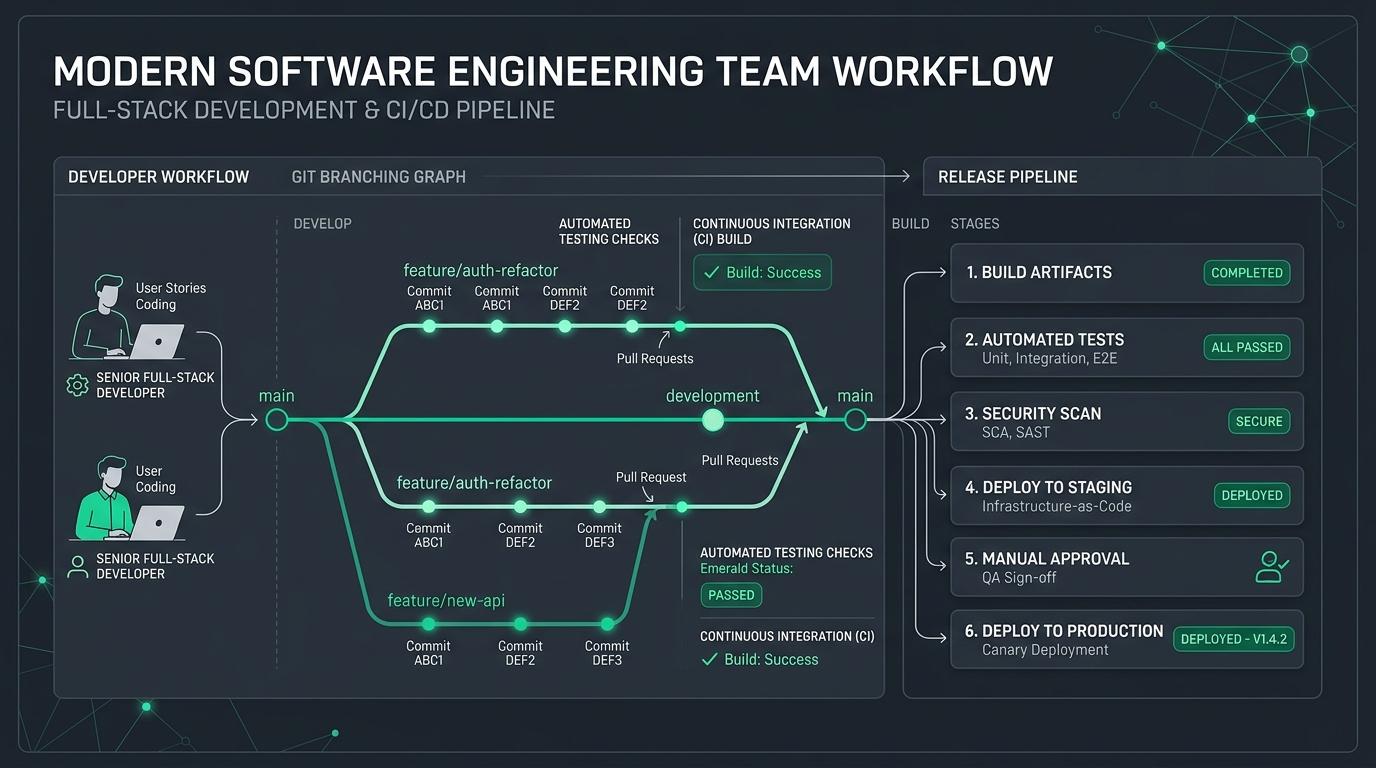
We lock data models, API contracts, and user acceptance criteria before writing code. You get an exact scope and fixed timeline.
Figma user flows and staging reviews so you see working interfaces before engineering spend expands.
Senior engineers push directly to your GitHub repository. Working code daily with clean pull requests and automated tests.
Zero-downtime production cutover, documentation handover, and a 30-day post-launch warranty with full code ownership.
Questions we hear on discovery calls—answered plainly.
Critical triage begins within hours. Complete cleanup and hardening typically finishes in 24 hours.
Hub: website-compromise-recovery. Explore the spokes and downloads buyers use before signing scope.
You get a fixed quote in 5 working days. Then a senior engineering team that ships.